PCI Compliance and The Potentially High Costs of a Breach
Last Updated on August 17, 2026 by Dimitri Akhrin
Protect Payment Data and Reduce Business Risk
Strong payment security helps businesses protect customer information and reduce the financial and operational risks associated with a data breach. PCI compliance provides a common security framework for businesses that handle payment account data.
Let’s talk about PCI Compliance. In the summer of 2019, it came out that Capital One, a credit card issuer themselves, fell victim to a hack that exposed the data of 100 million cardholders and applicants. That might seem extreme, but it’s only the latest in a series of high-profile security breaches that have resulted in the theft of personal data. In 2018, Marriott discovered a years-long breach that exposed the data of 500 million customers. In 2014 a breach exposed the data of 56 million Home Depot customers and a year before that, Target was hit with a hack that exposed 110 million customers. Other household names that have fallen victim to hacks in that time have included Yahoo, Adobe, eBay, Sony and more.
Updated context: The incidents above are historical examples from the original article. Payment security standards have continued to evolve since then. PCI DSS v4.0.1 is now the active version supported by the PCI Security Standards Council.
How PCI Compliance Protects Businesses
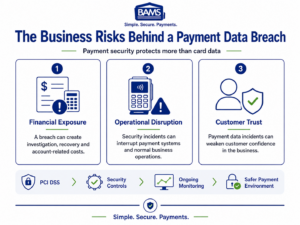
A payment data breach can create costs that extend beyond stolen information, making ongoing payment security an important business priority.
The reality is, data is extremely valuable and anything of value will always be the target of theft. You might be asking what chance your small business has if these behemoths can’t keep hackers out and it’s a valid question. First and foremost, the smaller you are, the less likely you are to be targeted, but the risk is always there. Beyond that, stopping data breaches all together isn’t realistically possible. But staying fully PCI compliant ensures that if for any reason there is a breach, your company will be able to show that you were fully on board with all rules and guidance and that will significantly minimize your exposure. Target, for instance, was fully PCI compliant and as such, the cost of its breach was small and insurance covered much of it.
Security Requires Ongoing Attention
Compliance should support an ongoing security program rather than function as a one-time task. Businesses still need to monitor their payment environment, control access to sensitive information and respond when technology or security risks change.
PCI compliance also does not make a business immune to a breach. It provides a security baseline that helps merchants reduce risk and demonstrate that they follow required payment data protections. Actual financial exposure after an incident can depend on many factors, including the circumstances of the breach, contractual obligations and insurance coverage.
What is PCI Compliance?
PCI compliance involves a business meeting a set of security requirements designed, mandated and administered by the five major credit card issuers: Visa, American Express, Mastercard, Discovery and JCB. The PCI security protocols aren’t required by law, but every business that processes credit card transactions and transmits or stores credit card payment data is required to be fully PCI compliant as part of their dealings with the credit card issuers. Failing to meet compliance standards can result in ongoing merchant account penalties, potential loss of an account altogether and hefty fines in the event of a breach.
Current PCI DSS note: Today, the PCI Security Standards Council defines PCI DSS as baseline technical and operational requirements designed to protect payment account data. PCI DSS applies to entities that store, process or transmit cardholder data or that can affect its security.
PCI SSC maintains the security standard while individual payment brands and acquirers determine merchant validation and reporting requirements. A merchant should confirm which compliance process applies to its specific payment environment.
What Merchants Should Review Today
PCI DSS v4.0.1 is the current version of the standard. Merchants should review their payment environment against current requirements rather than relying on an older compliance assessment.
The exact validation process can vary. Some merchants may qualify to use a Self-Assessment Questionnaire while other environments can require additional assessment or scanning. The merchant’s acquirer or payment brand can confirm the applicable validation requirements.
Businesses should also review changes to their systems throughout the year. Adding new payment technology, changing a website or connecting a new service provider can affect the payment environment and the controls a merchant needs to maintain.
How BAMS Helps Merchants Become Compliant
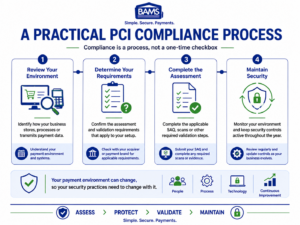
PCI compliance requires merchants to understand their payment environment, complete applicable validation and maintain security over time.
Becoming PCI compliant requires meeting a specific set of security standards and following a specific set of regular protocols to ensure ongoing security maintenance. Companies must analyze their existing compliance status, fill out an annual self-assessment questionnaire, identify any deficiencies in the 12 individual areas defined by the compliance protocol and remedy any they find. Once all that is complete, an attestation of compliance can be filed and the certification process completed. That process can be flummoxing for some businesses, especially new merchants just entering the world of credit card processing. At BAMS, we understand that confusion, so our reps walk each of our new merchants, step-by-step, through the compliance process to ensure that everything is done properly and that compliance can be achieved with minimal headaches and maximum efficiency.
BAMS currently helps merchants determine the appropriate Self-Assessment Questionnaire and complete the compliance process. Depending on the payment environment, merchants may also need regular vulnerability scans. BAMS provides guidance so businesses can identify the steps that apply to their setup.
Why PCI Compliance Still Matters After Certification
Completing an assessment does not mean a business can stop thinking about payment security. Employees, systems and technology can change throughout the year. Merchants should continue reviewing access controls, payment systems and security practices as their operations evolve.
Ongoing attention can also make the next compliance review easier. Businesses that maintain security practices throughout the year are better positioned to identify changes before they turn into larger payment data risks.
For more information on how BAMS can help your business get set up with a merchant account that will offer you the lowest possible fees and provide you with the step-by-step assistance, you need to ensure full PCI compliance, contact us today to speak to a member of our expert support team.
Frequently Asked Questions
What is PCI DSS?
PCI DSS stands for Payment Card Industry Data Security Standard. It establishes technical and operational security requirements designed to protect payment account data.
What version of PCI DSS should merchants follow?
PCI DSS v4.0.1 is the current active version. Merchants should use current requirements when reviewing their payment environment and validating compliance.
Does PCI compliance prevent every data breach?
No. Compliance provides an important security baseline, but no security program can guarantee that a breach will never occur. Merchants should maintain security controls throughout the year.
Does every merchant have the same PCI requirements?
No. The validation process can depend on factors such as transaction environment, payment methods and payment brand requirements. Merchants should confirm the applicable process with their acquirer or payment brand.
What is a Self-Assessment Questionnaire?
A Self-Assessment Questionnaire, or SAQ, allows eligible merchants to document how their payment environment meets applicable PCI DSS requirements. Different SAQs apply to different payment environments.
Can using a payment gateway remove PCI responsibilities?
No. Using secure payment technology can reduce a merchant’s PCI scope in some situations, but it does not automatically remove the merchant’s responsibility to maintain and validate compliance.
How can BAMS help with the process?
BAMS helps merchants work through the compliance process, including identifying the appropriate assessment steps and addressing requirements that apply to their payment environment.