How to Tell If Your Business Meets PCI Compliance
Last Updated on October 2, 2026 by Dimitri Akhrin
The Payment Card Industry Data Security Standard, or PCI DSS, is a security standard that every business accepting, storing, processing or transmitting card data from the major card brands has to meet. It exists to protect consumers and limit the damage from payment-related data breaches.
PCI compliance refers to a company’s ongoing work to maintain the physical and technical standards laid out in PCI DSS. The standard is organized into six goals and 12 principal requirements, covering everything from network security to physical access to company policies. Each merchant’s validation requirements depend on how many transactions it processes and how it handles card data. Needless to say, PCI compliance is complex. That causes problems because compliance is binary: a merchant is either compliant or noncompliant. There is no middle ground.
TL;DR
- PCI DSS applies to every business that accepts cards – Size doesn’t exempt you, though your validation steps depend on your volume and setup.
- Noncompliance puts your merchant account at risk – Acquirers are responsible for their merchants’ compliance and can pass along penalty fees or close risky accounts.
- Start by finding your compliance level – Card brands assign Levels 1 through 4 mostly by annual transaction volume and your acquirer can confirm yours.
- Most merchants validate with a Self-Assessment Questionnaire – The right SAQ depends on how your business handles card data, so choosing the correct one matters.
- You don’t have to do it alone – Your payment processor can walk you through the right level, SAQ and scans.
What Happens if Your Business Isn’t PCI Compliant
Failing to meet PCI standards carries real consequences and all of them put your business at risk. First and foremost, noncompliant businesses represent unnecessary risk. The OCC’s Comptroller’s Handbook on merchant processing describes PCI DSS as the standard a merchant must follow to accept payment cards and makes acquiring banks responsible for making sure the merchants they sponsor stay compliant. The card brands and your payment processor aren’t interested in taking on risky merchants, so failing to meet the standard could cost your business its merchant account.
Noncompliance can also be expensive. The same handbook notes that merchants can face penalty fees for violating card association rules or for fraud loss recovery after a data compromise. How much depends on the card brand, the acquirer and how serious and long-lasting the problem is.
Finally, failing to comply puts your business at greater risk of a costly data breach. Between customer lawsuits, damage to your reputation and the cost of remediation, a breach can cost a small business far more than staying compliant would have.
How to Tell if Your Business Is PCI Compliant
With so much at stake, taking your company’s PCI compliance seriously is a must. But with so much to know and so few merchants coming from technical backgrounds, how do you tell whether your business is compliant and, if it isn’t, what you need to do?
Determine Your PCI Compliance Level
The first step is to determine which PCI compliance level applies to your business. The card brands assign four levels, based mainly on your annual transaction volume. Definitions vary slightly by brand, but they generally look like this:
- Level 1: More than 6 million card transactions a year
- Level 2: 1 million to 6 million transactions a year
- Level 3: 20,000 to 1 million eCommerce transactions a year
- Level 4: Fewer than 20,000 eCommerce transactions or up to 1 million total transactions a year
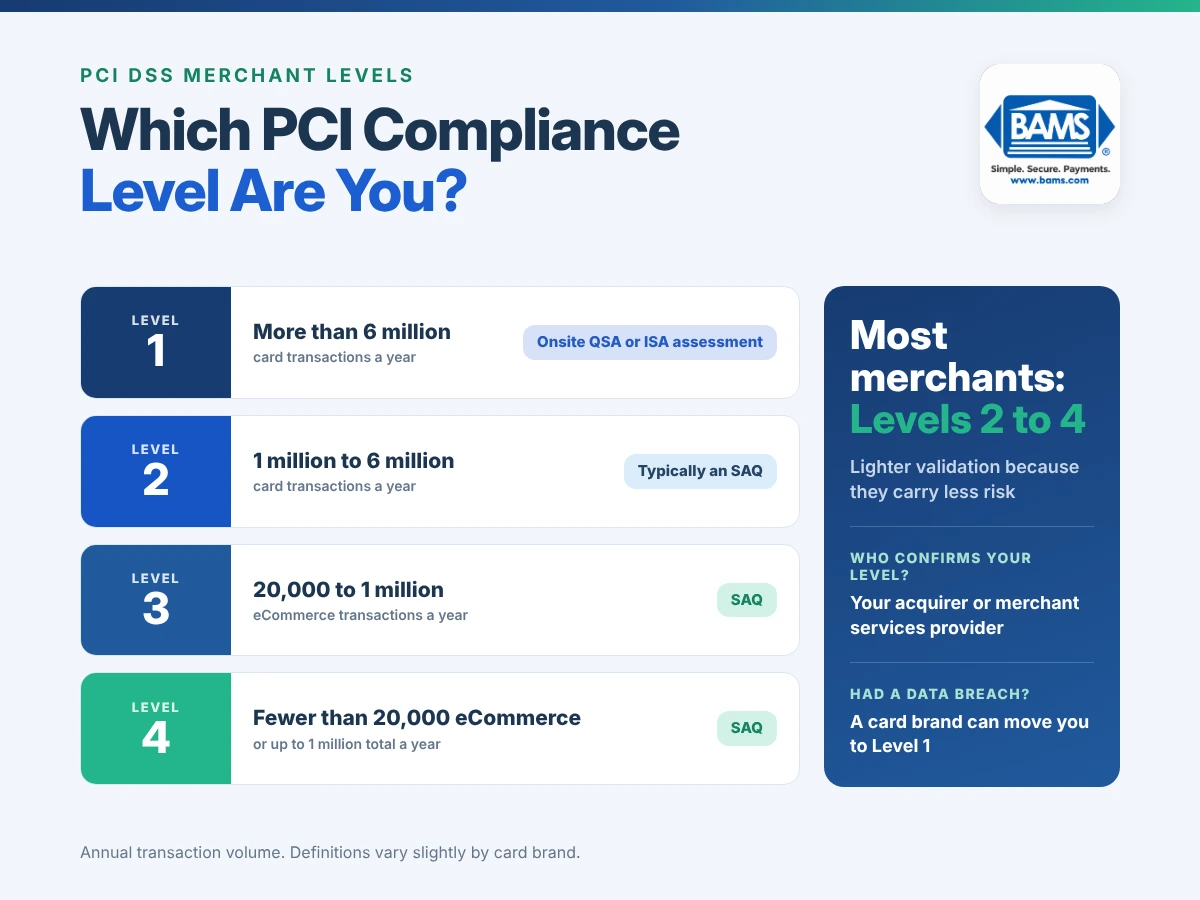
A card brand can also move a merchant that has suffered a data breach to Level 1, regardless of volume. The vast majority of merchants fall into Levels 2 through 4, which have lighter validation requirements because they carry less risk.
Your acquirer has the final word. According to the PCI Security Standards Council’s guidance for merchants, PCI DSS applies to all merchants regardless of size or transaction volume. Whether a smaller merchant must validate compliance is up to the individual card brands, so merchants should check with their acquirer or merchant services provider.
Complete a Self-Assessment Questionnaire
Level 1 merchants typically need an onsite assessment by a Qualified Security Assessor (QSA) or a trained Internal Security Assessor (ISA). At the other levels, you may only need to complete an annual Self-Assessment Questionnaire (SAQ). The SAQ is a tool that helps smaller merchants review their data security efficiently.
There are several types of SAQ and the right one depends on how your business interacts with customer payment data. A merchant that fully outsources online checkout uses a very different SAQ than one whose own systems capture card numbers. Even then, the PCI SSC FAQ on outsourced payment processing makes clear that merchants who outsource still have to validate their own compliance and confirm their providers are compliant. So make sure you’ve identified both your correct level and your correct SAQ. Many merchants with systems connected to the internet also need quarterly vulnerability scans by an Approved Scanning Vendor.
For a closer look at how your checkout setup affects which requirements apply, see our guide to avoiding dangerous gaps in PCI compliance.
Make Changes as Necessary
The Self-Assessment Questionnaire walks you through your company’s transaction security. If any gaps would cause you to fall short of the standard, the SAQ helps you find them. You then need to fix whatever part of your payment security fell short and complete the SAQ again to show full compliance.
How to Get Help with Achieving and Maintaining PCI Compliance
The SAQ is a useful tool, but PCI compliance is complex enough that many merchants never make it to the right SAQ, if they think about their PCI status at all. So if you’re not sure how to get started, don’t know which level or SAQ applies or think you need help, what should you do?
The good news is that you don’t have to navigate PCI compliance on your own. Your payment processor can offer the guidance you need to make PCI compliance less intimidating and help you meet the standard without pulling your hair out. If you’re unsure about the process, your first call should be to your account manager.
BAMS requires merchants to complete PCI DSS compliance within 90 days of approval and provides a guided process that includes the annual SAQ and quarterly security scans for merchants whose systems are connected to the internet. Our account managers get to know their clients’ businesses and can help make achieving and maintaining compliance much simpler. BAMS merchants also get transparent interchange plus pricing, which shows interchange and processor markup separately on every statement.
PCI Compliance FAQs
How do I know which PCI compliance level I am?
Card brands assign levels mainly by annual transaction volume. Most small businesses are Level 4. Your acquirer or merchant services provider can confirm your level.
Do small businesses need to be PCI compliant?
Yes. PCI DSS applies to all merchants that accept cards, regardless of size. Smaller merchants usually validate with a Self-Assessment Questionnaire.
What happens if I’m not PCI compliant?
You may face penalty fees, a higher risk of a data breach and the possible loss of your merchant account.
Which SAQ should I complete?
It depends on how your business accepts and handles card data. A fully outsourced online checkout, a card terminal and a merchant-built payment page can each require a different SAQ.
How often do I need to validate PCI compliance?
Validation is typically annual, with quarterly vulnerability scans for many merchants whose systems connect to the internet.
Sources
- Office of the Comptroller of the Currency – Comptroller’s Handbook: Merchant Processing
- PCI Security Standards Council – Merchant Resources
- PCI Security Standards Council – Outsourced Payment Processing and Merchant Responsibility
To find out how a BAMS merchant account can support your PCI compliance and how your current costs compare, request a free five-point Merchant Account Price Comparison.